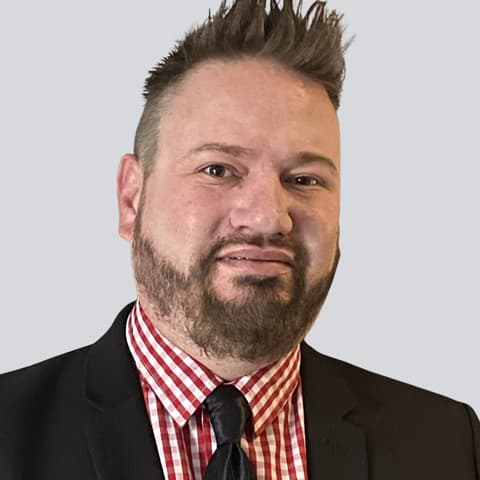
Donovan Francesco
Verified Expert in Engineering
DevSecOps and Security Architecture Developer
Johannesburg, Gauteng, South Africa
Toptal member since May 18, 2021
Donovan is a senior DevSecOps and cloud security architect with 24 years in IT. He helped deliver the first OpenStack public cloud in South Africa and has led infrastructure-as-code and security architecture rebuilds on AWS, GCP, and Azure using Terraform, Ansible, Chef, and Puppet. He has most recently applied that discipline to AI and LLM infrastructure, building agentic pipelines across Claude, ChatGPT, and Gemini, and is equally at home leading teams of 20 to 40 engineers.
Portfolio
Experience
- DevOps Engineer - 10 years
- DevSecOps - 10 years
- Amazon Web Services (AWS) - 8 years
- Google Cloud - 7 years
- Terraform - 7 years
- Kubernetes - 7 years
- Ansible - 7 years
- Google Cloud Platform (GCP) - 5 years
Work Experience
Senior Operability Engineer
AXA UK
- Hardened and automated the platform across Azure APIM, App Gateway, and ASE.
- Developed policy-as-code to deploy Dynatrace OneAgent site extensions across 2,000 App Service web apps and Function Apps.
- Migrated legacy ARM VM/VMSS fleets to Bicep with auto-enrollment into Microsoft Entra ID for Windows Server 2025.
- Refactored Azure Front Door ASE back-end routing using ARM/Bicep and integrated Application Gateways over Private Link.
- Automated cross-org federated identity, moving Databricks-to-SQL connectivity off the public internet onto Private Link.
- Implemented KEDA-based autoscaling on the automation pipeline.
- Built advanced agentic pipelines across Anthropic Claude, OpenAI ChatGPT, and Google Gemini, authoring agentic loops and a graph knowledge base to improve performance with token optimization and caching techniques.
- Automated code review with agents in GitHub Actions that helped developers catch mistakes early, cutting PR review turnaround by 70%.
Senior DevOps Engineer
The Vitality Group
- Remediated Google Security Command Center findings to bring the GCP platform into GDPR compliance.
- Applied VPC Service Controls to deny traffic to public DNS, allowing access only to the internal Google Container Registry (GCR).
- Enforced virtual perimeters around BigQuery, Cloud Storage, and Vertex AI to block data exfiltration and deny access to private data even with stolen IAM credentials.
- Restricted data access and traffic flow to authorized geographic regions and corporate networks.
- Deployed Palo Alto VM-Series in-line inspection (NSI) across four regions (South Africa, Belgium, Singapore, and us-central1), inspecting east-west inter-region traffic over Google Cloud Network Connectivity Center.
- Automated zero-touch Palo Alto provisioning, bootstrapping installation, configuration, and automatic licensing across the environment.
- Was one of the first adopters/implementers of GCP Network Connectivity Center (NCC) with hybrid inspection topologies, running Google's Fabric Fast Terraform design on Terraform Cloud workspaces.
- Ran CUDA/GPU-enabled workloads on Google Kubernetes Engine (GKE).
Senior Observability Engineer
Cline Bot Inc.
- Designed and implemented observability architecture (metrics, logs, traces, events) across all services; instrumented distributed systems and AI inference pipelines for root-cause analysis and performance optimization.
- Built Terragrunt/Terramate IaC for multi-region GCP, and secured ingress with GCP Cloud Armor WAF-as-code and GLB/GCE/NLB.
- Introduced a biweekly release cycle with GitHub Actions for CI and GitOps via ArgoCD and Helm for CD, cutting deployment risk by more than 80% for core systems.
- Improved Helm charts with better templating, enabling GCP Gateway API ingress on Kubernetes and OIDC federation via the Google identity provider.
- Defined SLIs, SLOs, and SLAs for critical LLM-provider and intrusion-detection services.
- Paired SRE practice on Grafana Cloud with Datadog SIEM for SOC 2 compliance, plus Aikido DAST and Vanta for security remediation.
- Built dashboards, alerts, and tooling for developers, SREs, and leadership, working cross-functionally to remove incident-response bottlenecks.
- Managed dynamic node provisioning and node-pool scaling with Karpenter.
Senior Operability Engineer
Waitrose & Partners
- Owned architecture, security systems, and networking across 8 EKS platforms on an AWS-first platform team.
- Ran GitOps deployment with ArgoCD, Helm, Terraform, GitLab, and Jenkins pipelines across the platforms.
- Automated day-to-day operations with Slack bot workflows.
- Applied Kyverno security policy to the EKS clusters and led the migration from OPA Gatekeeper to Kyverno.
- Delivered over 15 tailored Kyverno policies across 8 EKS clusters.
Principal Technical Lead for DevSecOps
BancX
- Led 10 direct reports to cut time-to-deploy by more than 50% across Spring Boot, Node.js, Ansible, and Python, entirely on Azure.
- Authored 17 Terraform modules and wrote Ansible playbooks following best-practice design and security, passing SOC 2 compliance.
- Patched and maintained Azure Red Hat OpenShift across three fleets, then spearheaded the migration to Azure Kubernetes Service.
- Reduced technical debt and complexity by 80%, delivering applications and infrastructure with Terraform, Helm, and ArgoCD.
- Deployed Prometheus, Thanos, Grafana, Loki, Tempo, and Alertmanager for telemetry and monitoring.
- Migrated over 65 microservices to ArgoCD and Helm so developers could self-serve deploys into DEV/UAT/Production.
- Deployed Azure App Gateways with Keystore for SSL and API Management with scoped tokens/permissions for customers.
- Built an OWASP-aligned WAF and created SIEM auditing. Used Infracost with Terraform to plan capacity and manage FinOps costs.
- Implemented the monitoring and alerting stack with Grafana, Loki, Prometheus, Alertmanager (WhatsApp and Slack), and Thanos on Azure Blob Storage, cutting mean time to respond and resolve from 3-5 days to 4 hours.
- Drove unit, smoke, integration, and end-to-end testing with GitHub Actions, integrating Playwright for UX testing and cutting PR review time from 2 days to 8 hours.
AWS DevOps Engineer
CapitalRise Finance Limited
- Redesigned the AWS infrastructure end to end and implemented it, moving it onto a modern, highly available footing.
- Advised on best practices for containerizing their application with Docker, then carried the change through to production deployment.
- Took the platform infrastructure-as-code with Terraform, wiring CI/CD through Bitbucket Pipelines, GitHub Actions, AWS CodePipeline, and CodeBuild.
- Integrated ArgoCD with Helm charts, cutting the deploy feedback loop by an order of magnitude.
- Brought a security-first lens to the build, with an eye on regulatory compliance, given the financial sector.
- Used Ansible to bring every environment to the same state, with centralized logging and health checks via Promtail and Grafana.
- Configured monitoring and analytics so the new platform was observable from day one.
- Documented the architecture and operational runbooks in Confluence and tracked the delivery through Jira.
Azure DevOps
Hearst
- Wrote modular and reusable Terraform modules for deploying large language models (LLMs) on Azure, AWS, and GCP.
- Built CI/CD pipelines with GitHub Actions, Terraform, and Helm/ArgoCD for blue, green, and canary deployments.
- Deployed an observability stack across all clusters and services with Datadog and New Relic.
- Set up the environments backing the GenAI proofs of concept for several business units.
- Worked alongside the project sponsor to stand up each PoC environment and convince the board.
Senior Site Reliability Engineer
Curology
- Wrote Helm charts for multiple teams and streamlined their ArgoCD GitOps workflows.
- Modernized Terraform modules that hadn't been touched in years.
- Integrated infrastructure with Cloudflare and Terraform to automate and audit changes on their content delivery network.
- Automated Datadog dashboards and synthetic tests as code via Helm/Argo and Terraform, wired alerting into Slack, and extended observability across all systems.
- Owned the cloud portion of the stack on AWS (EKS, ACK) and worked across the backlog to raise SRE best practices.
- Wrote runbooks and documentation, and produced architecture diagrams for the platform.
DevOps | System Administrator
DigiTrails SA
- Rebuilt the entire infrastructure and SDLC in Terraform with Git as the source of truth; set up GitHub Actions and Terraform Cloud pipelines for IaC and a GitOps platform on ArgoCD.
- Wrote Helm charts for streamlined deployment, rollback, and production code releases.
- Developed 20 Ansible roles and playbooks to provision and secure on-site equipment.
- Built OWASP and PCI/DSS best practices into the delivery pipelines.
- Configured and maintained the Debian appliance fleet, installing and wiring services and connecting the machines so the whole cluster is reachable through a single API; handled Linux setup and networking across the devices.
AWS DevOps Engineer
Prometheus Technologies Ltd
- Reviewed the AWS-based setup (EKS, RDS/Postgres, self-hosted Hasura GraphQL, SaaS Confluent Kafka, Lambda and SQS) and proposed workload-estimated changes for security, scaling, and cost-efficiency to get production-ready.
- Built the entire infrastructure as code in AWS with Terraform and Terraform Cloud, spanning 20+ modules and adaptable for production, staging, and dev.
- Authored Helm3 templates across more than 10 projects deployed to AWS EKS via Argo CD.
- Created Terraform Cloud manifests with encrypted secrets via AWS Secrets Manager, exposed to pods at runtime through the Kubernetes CSI driver.
- Implemented a least-privileged access model with IAM policies and scoped service accounts.
- Ran SAST (SonarQube, Anchore) and DAST (Snyk) scanning of application code and container-based image risk assessments.
- Developed and deployed Confluent Kafka and Atlas MongoDB Terraform modules over AWS PrivateLink.
- Applied and documented the agreed points with full hand-over documentation for maintenance by future DevOps engineers and developers.
Senior Systems and DevOps Engineer
MAS S.A.
- Deployed Kubernetes to bare metal using Ansible (Kubespray) with Terraform holding deployment state and version control; also wrote Terraform modules to migrate the customer's stack into Azure, including a move from native Kubernetes to AKS.
- Wrote Helm charts for the customer's in-house software, deployed and versioned via Argo CD.
- Ran GitHub Actions pipelines for build, test, SAST, smoke tests, and promotion; modernized GitLab CI/CD with Snyk scanning and layered in Anchore image scanning to catch container vulnerabilities before release.
- Performed post-scanning of built images using Anchore and Tenable Nessus, and liaised with auditors and pen testers to close procedural and technology gaps.
- Cut a production Docker image from 2 GB down to 500 MB by trimming layers.
- Applied DRY methodology across the pipeline, taking 60%+ off time-to-deliver, backed by quality gates on code smells, complexity, and security hotspots.
- Wired Terraform into Azure services directly: AKS, Keyvault, Azure Active Directory, Azure DNS, VNet peering, VPN peering, and ACR.
- Deployed Prometheus, Thanos, Grafana, Loki, Tempo, and Jaeger, plus MinIO for S3 blob storage, aggregating metrics and logs into a sysops command center. A single pane for bugs and resource contention cut time-to-resolution by more than 40%.
- Integrated the ELK stack with a machine-learning module to flag anomalies, and made sure the Kafka message bus could durably back up its topics and queues.
- Managed and automated the service lifecycle across the fleet, monitoring live and remote production systems, running audits, and drafting service documentation to improve reliability and performance.
DevOps and Kubernetes Engineer
Pano AI, Inc
- Built the infrastructure in Terraform to Google's best practices and to ISO 27001, PCI, and DSS compliance; rewrote the existing Terraform (50 modules) to be fully idempotent and integrated it with Terraform Cloud.
- Ran Terraform Cloud with workload identity and short-lived service accounts across workspaces, with encrypted variables and remote state.
- Built GitHub Actions pipelines for build, test, and SonarQube static analysis.
- Used Jaeger tracing with Grafana Tempo and Loki for event monitoring.
- Used Terraform workspaces to split dev, staging, and production environments.
- Improved the continuous deployment pipelines with Helm 3, and put Argo CD in front of Helm so releases stayed versioned and reflected in source control.
- Autoscaled infrastructure on custom Stackdriver metrics based on application load and load-balancer HTTP requests; added Infracost so the team could see plan cost before applying.
- Built the GCP environment with Cloud SQL, Cloud Load Balancing, Pub/Sub queues, GCS, and Prometheus monitoring and alerting across GKE node pools.
- Created VPC peering, Cloud DNS changes, Slack alerting, PagerDuty on-call integration, Cloud Functions, WAF with rules, and Loki integration with Stackdriver.
- Managed a multi-cluster, multi-node-pool GKE footprint, defined the infrastructure roadmap with diagrams, and took on-call rotation to triage production issues.
Site Reliability Engineer
Sandhills Global
- Kept applications PCI compliant across Windows Server and Linux, with documentation, application-flow diagrams, and system architecture. Was trusted with access to the Card Data Environment (CDE) to ensure security controls were in place.
- Built environments on the Cloud Adoption Framework for Terraform: VNet, VNet peering, resource groups, DNS records, AKS, firewall policies, identity management, and app service plan deployment on Azure DevOps.
- Automated a "click-ops" Azure Portal environment, writing Terraform modules and CI/CD pipelines for their future state, deploying Azure Front Door (CDN), and setting up User Assigned Identity, Keyvault, and Azure DNS.
- Designed and implemented the DR plan and ran cost-optimization exercises to show return on investment.
- Wrote custom modules in TypeScript and C# for the in-house CRM and planning tool.
- Ran penetration tests, including fuzzing and reverse-shell exploitation with Kali Linux, Metasploit, and OWASP ZAP.
- Put Istio in place for east-west security controls, including OPA inside AKS, and managed F5 and checkpoint appliances.
- Wrote CI/CD pipelines on Azure and worked across Azure services and networking to improve systems and document how things run.
- Applied DRY methodology to cut delivery/deploy time by 60%+ with quality gates on code smells and complexity, and used Anchore to catch container vulnerabilities before shipping. A Grafana/Loki/Tempo/Jaeger stack cut time-to-resolution by over 40%.
- Migrated apps from Azure DevOps into Helm deployments, replacing App Insights with Prometheus, Grafana, Loki, and Tempo for observability, with remote state moved from a storage blob container to Terraform Cloud.
Principal Technical Lead for Automation
Yoyo Group
- Owned technical design and implementation for a platform serving 3 million+ users, leading 20 direct reports.
- Sponsored and led the migration of 700+ repositories from Bamboo/Jenkins to GitHub Actions.
- Rearchitected monolith applications into a microservices-based architecture.
- Rewrote CloudFormation scripts into Terraform for infrastructure-as-code.
- Applied AWS patterns with Terraform/Terragrunt for IaC; set AWS networking, security, and deployment methodology across ECS (Fargate), RDS, EC2, NLB/ALB, target groups, and auto-scaling groups.
- Implemented SonarCloud in GitHub Actions to enforce quality gates that blocked failing deployments.
- Ran security and dependency scanning (SonarQube, Anchore, Tekton CI, ArgoCD, EKS) to keep only clean images in ECR.
- Oversaw security and architectural design for ISO and SOC 2 compliance requirements.
AWS DevOps
Azrieli Group
- Migrated EC2 and Fargate components to EKS-managed node pools using Terragrunt, with security, monitoring, dashboards, and secret management in place.
- Reworked the Terraform structure to align with best practices and moved Terraform state from S3 to Terraform Cloud.
- Built the infrastructure with Terragrunt and Terraform across AWS to support 10,000 requests per second.
- Kept CI/CD zero-touch and versioned with Argo CD and Helm 3, running the Atlantis PR workflow on AWS Fargate.
- Wired AWS Secrets Manager to pods via the CSI driver, converted CloudWatch logs to Grafana Loki, and used Lambda to reshape log output for Loki.
- Tightened IAM roles, security policies, and audit trails across the AWS account.
- Added Anchore for container vulnerabilities and Infracost to show plan cost, and ran FinOps cost analysis via Optscale.
- Wrote Terraform from scratch for AWS ACM, CloudFront, ECR, EFS for multi-pod persistent storage, and EKS with cert-manager and ExternalDNS; used Terraform and Elasticsearch to control Route53.
- Wrote documentation and runbooks for the operations team and introduced managing sensitive credentials and API keys via the CSI driver against AWS Secrets Manager.
Senior DevOps Engineer
TetraScience
- Improved dev velocity with Terraform and a GitHub Actions/Atlantis PR workflow for infrastructure changes.
- Ran the operational-readiness lifecycle end to end, from design through deployment and refinement, with automated, self-healing tooling to keep systems resilient and minimize human intervention.
- Spun up VPC, Amazon Aurora, PostgreSQL, DocumentDB, Redis clusters, and security groups with Terraform, and migrated from eksutils to Terraform.
- Tested and rolled out node pools for EKS 1.16, then upgraded EKS to 1.21.
- Migrated self-managed Redis and MongoDB to AWS-managed Redis and Amazon DocumentDB, a real step-change for high availability.
- Closed off a credential-leak risk by wiring AWS Secrets Manager into EKS via the CSI driver, so no password or API key ever passed unencrypted.
- Documented DevOps/DevSecOps best practices for a hybrid AWS/OSS stack, introducing Prometheus, Grafana, Thanos, and Loki, and helped ensure monitoring and metrics were built into applications before production.
Director of DevSecOps and Security Architecture
DotModus
- Led a team of 20 senior DevOps engineers across client engagements.
- Served as senior security lead at Dentsu, a global media company and Dotmodus client, running purely on Azure; approved design patterns as a member of the Technical Design Authority (Global).
- Implemented a secure software delivery lifecycle framework; identified critical CVEs and designed a policy to minimize blast radius.
- Ran honeypot environments and Chaos Monkey red-team drills against SLAs.
- Architected federated identity with Okta across Azure AD, Google IdP, and AWS SSO, with automation enabling the migration of over 65,000 users with their claims and permissions to downstream APIs and front ends.
- Enforced GDPR/PII/HIPAA/POPI encryption in flight and at rest across AWS/GCP/Azure.
- Secured federated GraphQL against nested queries, SQL injection, and schema introspection using OWASP GraphQL best practices, running penetration tests and enforcing query-depth and introspection limits.
- Architected perimeter and API defense for ingress and egress with API gateways and service meshes, introducing policy-as-code and GitOps across a multi-country organization, with automated whitelisting, blacklisting, and path-based routing.
- Delivered a mobile banking app deployment on AWS using CodeCommit, CodeBuild, CodePipeline, Device Farm, and Amplify, with S3 build artifacts and CloudFormation-provisioned test projects.
Principal Technical Lead, Platform Engineering and Security
Dimension Data
- Led a team of 30+ engineers and managed two business units' budgets and planning, including strategic execution of critical projects and defining reporting-line structures.
- Designed and implemented security policies and frameworks to raise compliance for external auditing companies, and educated executive leadership on ISO 27001, NIST CSF, and PCI DSS.
- Introduced low-interaction and pure honeypots alongside high-interaction demarcated zones; owned security tracing through the delivery lifecycle and reviewed asset and operational risk controls.
- Upgraded OpenShift from 3.9 to 3.11 (design, documentation, implementation, and operations), upgraded the Ceph storage platform (700+ TB), and provided S3-compatible object storage via Ceph RADOS.
- Upgraded the OpenStack platform from Icehouse to Juno for 700+ customers and implemented Metal-as-a-Service to speed up turnaround for customers interfacing with the data-center engineering team.
- Defined compliance and governance standards for ISO accreditation, and improved SLA management across business and technical requirements.
- Led migration of over 1,000 virtual machines from VMware on-premise to AWS, using HashiCorp Packer for Golden AMIs and AWS Control Tower for multi-account governance.
- Migrated services from hosted VMs to Amazon EKS with Terraform and Terragrunt across multiple accounts and regions, using AWS Redis, Aurora, CloudFront, Lambda, and GitHub Actions.
- Deployed the Istio service mesh inside Kubernetes and authored infrastructure-as-code with architecture diagrams.
- Enforced GDPR, PII, HIPAA, and POPIA policies to encrypt data in flight and at rest, and maintained VMware patching and SAN storage on fiber-channel EMC arrays.
Principal Technical Lead, OSS
Dimension Data
- Managed the network monitoring team covering 65,000+ endpoints.
- Led the architecture and engineering team, training engineers from the front.
- Oversaw security for the EMEA region and led architecture and solution design with Cisco to securely deploy and automate the network using SDN.
- Owned network, platform, cloud, application, and middleware security architecture, plus identity and access management.
- Architected bespoke customer solutions on legacy systems and industrialized modern go-to-market services on public cloud, including migrations to AWS and GCP with SSO.
- Drove projects using Agile methodology, presenting live demos to executives and managing large budgets.
- Applied VMware patch and security updates, maintained system diagrams and documentation, and handled Windows Server updates with IIS and terminal-services load balancing.
- Enforced GDPR, PII, HIPAA, and POPIA policies, encrypting data in flight and at rest.
Cloud Architect, Infrastructure and Security
Dimension Data
- Helped deliver the first OpenStack public cloud in South Africa using OpenStack and Ansible.
- Instrumented the platform with Prometheus for agent and API scraping, visualized through Grafana.
- Operated a public cloud for 1,000+ customers, owning architecture, operations, and maintenance for the cluster.
- Designed the automation pipeline with Ansible and Jenkins, using custom code to call the OpenStack APIs and deploy VMs on behalf of customers.
- Architected cloud migration strategies with a focus on security, supporting cross-functional teams on strategy and operational issues.
- Conducted penetration testing with Kali Linux, Metasploit, OWASP ZAP, and Burp Suite Pro, writing fuzzing and reverse-shell exploits.
- Automated Windows and Windows Server rollouts for CI/CD pipelines, and managed and supported the VMware cluster.
- Built the system architecture design using AD FS and single sign-on.
Senior Cloud Support Engineer
Amazon Web Services (AWS)
- Served as subject matter expert for Linux and RDS on the senior support team.
- Assisted enterprise customers migrating workloads from on-premises to the public cloud.
- Built SME depth in EC2 and RDS, the engagement that shaped a later move into GCP and Azure architecture work.
- Supported customers across VPC, VPN IPSEC, EC2 Linux/Windows, ELB, Auto Scaling, and CloudFormation.
- Covered CloudWatch/Alarms, RDS, Route53, S3, CloudFront, IAM Policies, and WorkSpaces.
Executive Manager, Systems
DNS Solutions ZA
- Managed the deployment of multiple OpenStack IaaS environments, giving developers infrastructure-as-a-service to deploy code through a Jenkins automation pipeline.
- Deployed multiple OpenStack environments so developers could self-serve infrastructure.
- Automated infrastructure deployment through a Jenkins automation pipeline.
- Started on Puppet, but its DSL and parallelism model got in the way; switched to Ansible for high-velocity automation and ease of use.
- Integrated Windows AD into 389-DS so Linux machines authenticated via LDAP.
- Trained and mentored mid-level engineers and helped architect a multi-datacenter solution for resiliency.
Senior Systems Manager
Open Network Holdings
- Built a computing platform handling various workloads, automating infrastructure and networking deployments, and trained and mentored junior engineers.
- Contracted to build a computing platform for varied workloads in the early days of cloud computing; automated infrastructure and networking deployment.
- Built the team's own CI/CD platform on Jenkins, automating build and package, and used Puppet to deploy artifacts.
- Worked with OpenStack, Ceph, InfiniBand HPC networking, GlusterFS, Perl/Bash scripting, KVM, Splunk, and centralized logging.
- Introduced an SDLC process where every artifact passed through vulnerability, coverage, and app-hygiene checks before release.
- Delivered an OpenStack private cloud for the organization and trained and mentored junior engineers.
Network Security Manager
ECN Telecommunications
- Built the core VoIP infrastructure across multiple regions, solely responsible for its automation and security.
- Automated mass configuration across more than 400 remote servers with Puppet, including OpenVZ, VMware, and KVM virtualization.
- Delivered a redundant, load-balanced platform using Red Hat Cluster, DRBD/iSCSI/SAN, ldirectord, and HAProxy, with MySQL Cluster (NDB) for high availability.
- Integrated Snort IDS, Radius, and MySQL, Bacula backup, and Eucalyptus hybrid-cloud configuration.
- Secured the network with white-hat tooling and principles against malicious attacks, and implemented FCAPS management (fault, configuration, accounting, performance, security).
- Ran penetration tests, including fuzzing and reverse-shell exploitation, with Kali Linux, Metasploit, OWASP ZAP, and Burp Suite Pro.
IT Manager
M & D Laminates
- Built a hub-and-spoke network allowing multiple branches to connect and use internal business applications. Trained and supported junior engineers and shared knowledge regarding system architecture and network design.
- Used different technologies, from Linux servers that managed incoming sessions and firewalling to email and web hosting linked to the Microsoft Active Directory.
- Improved remote work for the company, which allowed the business to accelerate its vision.
- Supported development and submissions of budgetary and investment plans.
- Designed security architecture elements to mitigate threats as they emerge.
Linux and Windows Engineer
Networks Online
- Contributed to supporting and maintaining onsite client solutions. Supported bespoke customer requirements.
- Attended to roughly 40 clients, remotely and onsite, ranging from network, VLAN, and segmentation to DBA administration and domain controller policies.
- Configured and maintained a large-scale VPN deployment with webpage caching.
Linux and Windows Engineer
SA Feed
- Managed all IT administration and configuration and a few Linux servers that provided website hosting, firewalling, and secure access to network-provided storage.
- Used technologies, such as iptables firewall, Samba domain controller, Qmail, Windows support, PC hardware support, Apache web servers, Squid proxy servers, and Bind8 (DNS).
- Managed all IT operations of the company, increasing accessibility to business-critical services, and improving the user experience.
- Supported cross-functional teams to investigate, analyze, and make recommendations to leadership on the strategy or operational issues.
Project History
Venture-backed Startup
https://pano.aiThe project was done entirely in GCP, using Cloud SQL, Cloud Load Balancing, Pub/Sub queues, GCS, Prometheus monitoring and alerting, GKE with GKE node pools, and custom metrics with Stackdriver to scale under specific affinity rules in Kubernetes. I used GitHub Actions and Helm 3 to deploy applications to the clusters. I created VPC peering, Cloud DNS changes, Slack and PagerDuty integrations, Cloud Functions, WAF with rules, and Loki integration with Stackdriver.
Kubernetes on Bare Metal
https://maseurope.comThe customer needed their team to upgrade Kubernetes and use versioning to roll out applications with different configurations. I implemented Helm 3 to deploy their software via VPN from their internal GitLab CI instance, writing over 12 Helm charts for each software component, and used GitLab CI to follow the standard SDLC pattern: build, test, quality-scan, vulnerability-scan, upload a new Docker image, then trigger Anchore to scan the uploaded image.
Once versioning was in place, I deployed Argo CD to the clusters so it controlled the running configuration, with synchronicity facilitated by Git source control. Then, I deployed Prometheus, Thanos, Grafana, Loki, Tempo, and MinIO for S3-compatible blobs, aggregating metrics and logs to a command center so sysops could monitor and control everything from one place.
SRE and Automation
https://sandhills.comI implemented the Cloud Adoption Framework to stay aligned with Azure's best practices and policies. Deployed management groups, VNets, VNet peering, Azure firewalls, and dynamic Key Vaults. The remote state started in a storage blob container and was later moved to Terraform Cloud. I was also part of the day-to-day operations and reliability team, aided the PCI compliance team in achieving their goals, and was trusted with access to their card data environment (CDE).
Migration of EC2 Services to EKS
https://www.azrieli.com/Supporting services for their main applications, written in PHP, included writing Terraform code from scratch for AWS ACM, Amazon CloudFront, ECR, EFS for multi-pod persistent storage, and EKS with Prometheus, Alertmanager, cert-manager, ExternalDNS, Thanos, and Grafana for alert aggregation. I also wrote Cloud Functions to convert Amazon CloudWatch logs into a format that Grafana Loki could index and used ExternalDNS to manage Route 53 records. I wrote documentation and runbooks, and introduced the team to managing sensitive credentials and API keys by implementing the CSI driver against AWS Secrets Manager.
EKS Upgrades and Managed-service Migration
https://www.tetrascience.com/I controlled EKS upgrades and added managed node pools using Terraform, and oversaw reliability and testing of upgrades from Kubernetes 1.16 to 1.21. I wrote a GitHub action to make release pipelines easier to manage and test. The Terraform code also spun up VPC, Amazon Aurora, PostgreSQL, DocumentDB, Redis clusters, and security groups, and migrated existing Redis clusters into AWS-managed Redis clusters with high availability.
Migration to AWS and Microservices
I migrated over 700 repositories from Bamboo/Jenkins to GitHub Actions, rewrote all CloudFormation scripts into Terraform, and implemented SonarCloud in GitHub Actions to enforce quality gates that blocked deployments. I educated and trained developers on microservices architecture and, just as importantly, which workloads should not be put into containers.
Perimeter and API Defense
http://www.dentsu.comI worked across multiple teams to keep the project moving with the least friction, managing budgets and resources while also writing the actual code to get the project over the line for a third-party client. I introduced automation for whitelisting ingress and blacklisting egress to known bad actors, and established path-based routing to enforce security policies between logical zones of clusters.
Network Security Inside a Service Mesh
https://www.dotmodus.com/Federated Identity with SSO
https://www.dotmodus.com/Mobile Bank App Deployment
https://www.dotmodus.com/AWS Lambda functions invoked the Device Farm test from CodePipeline and provisioned the Device Farm project from AWS CloudFormation. The design also included AWS Amplify for writing modern UI-driven, scalable client-server applications across major languages and platforms. I was also responsible for identifying, communicating, and maintaining awareness of current and emerging security threats and industry trends, including flagging security design gaps in existing and proposed architectures and recommending changes.
Federated GraphQL Security
https://www.dotmodus.com/I conducted penetration tests against the federated GraphQL and downstream services and uncovered query depth limits and introspection weaknesses that could be used to enumerate queries against the graph. I wrote a GraphQL policy and blueprint that the global organization implemented to secure GraphQL endpoints.
Migration Services to Amazon EKS
https://www.dimensiondata.com/On-premise Migration to Public Cloud
https://www.dimensiondata.com/This was a long project, almost a year, due to customer availability. I introduced HashiCorp Packer to build Golden AMIs and took care of network, security, and access control throughout. Over the program's lifecycle, I migrated all customers to AWS with the help of AWS Control Tower.
DevOps Leadership and SOC 2 on Azure
https://bancx.comGCP GDPR Compliance and Network Security
https://vitalitygroup.comObservability and IaC for an Open-source AI Coding Agent
https://cline.botI built Terragrunt and Terramate IaC for multi-region GCP, secured ingress with GCP Cloud Armor WAF-as-code and GLB/GCE/NLB, and introduced GitOps with GitHub Actions for CI, as well as ArgoCD and Helm for CD on a biweekly release cycle, cutting deployment risk by more than 80% for core systems.
I defined SLIs, SLOs, and SLAs for critical LLM-provider and intrusion-detection services, paired SRE practice on Grafana Cloud with Datadog SIEM for SOC 2 compliance, and managed dynamic node provisioning and node-pool scaling with Karpenter.
Azure Platform Hardening and Private Link Automation
https://axa.comEducation
High School Diploma in Computer Science
ACE Christian Academy - Johannesburg, South Africa
Certifications
Red Hat Certified Engineer (RHCE)
Red Hat
Red Hat Certified System Administrator (RHCA)
Red Hat
Sair Linux and GNU Certification
INTEC Education Group
Skills
Libraries/APIs
Node.js, Thanos
Tools
Terraform, Ansible, Git, Cron, Helm, Nagios, AWS ELB, Grafana, Subversion (SVN), RabbitMQ, MQTT, Amazon Simple Queue Service (SQS), Amazon CloudWatch, AWS Fargate, Jenkins, CircleCI, Azure Kubernetes Service (AKS), GitHub, GitLab CI/CD, Amazon EKS, Squid Proxy Server, NGINX, Amazon Elastic Container Service (ECS), AWS CloudFormation, Amazon Virtual Private Cloud (VPC), AWS IAM, Logging, Confluence, Amazon Cognito, Splunk, Istio, Grafana k6, Kubernetes HorizontalPodAutoscaler (HPA), Google Kubernetes Engine (GKE), Azure Application Gateway, Claude, ChatGPT, GCP Network, GCP Security, Amazon Simple Notification Service (SNS), SonarQube
Languages
Bash Script, Bash, Python 3, Python, SQL, PHP, TypeScript, Java, Go, Bicep
Paradigms
DevSecOps, DevOps, Azure DevOps, Continuous Integration (CI), Continuous Development (CD), Continuous Delivery (CD), Microservices Architecture, Global Server Load Balancing (GSLB)
Platforms
Kubernetes, Google Cloud Platform (GCP), Azure, Amazon Web Services (AWS), Docker, Apache Kafka, Linux, Azure IaaS, AWS NLB, OpenShift, Rancher, Amazon EC2, AWS Lambda, AWS IoT, Graphy, NVIDIA CUDA, Vertex AI
Storage
Google Cloud, MongoDB, MySQL, Google Cloud Storage, Data Centers, IIS SQL Server, Elasticsearch, Amazon Aurora, Databases, Amazon S3 (AWS S3), PostgreSQL, Datadog, Redis, Azure SQL Databases
Industry Expertise
Cybersecurity
Frameworks
Windows PowerShell, .NET, Ruby on Rails (RoR)
Other
DevOps Engineer, CI/CD Pipelines, Site Reliability Engineering (SRE), System Administration, Cloud Services, Networking, Virtualization, Monitoring, Cloud Security, Shell Scripting, HAProxy, Infrastructure as Code (IaC), User Stories, Virtual Machines, Azure Virtual Machines, Firewalls, AWS DevOps, Configuration Management, Application Security, Web Security, Security, Identity & Access Management (IAM), Architecture, Load Balancers, Cloud, Agile DevOps, Amazon RDS, K3s, TCP/IP, Proxies, WebSockets, Argo CD, Containers, Cloud Infrastructure, Cloud Architecture, Distributed Systems, Virtual Private Cloud (VPC), Artificial Intelligence (AI), Project Management & Delivery.Project Management, Product Management, ECS, Software Engineering, Large Language Models (LLMs), Project Management & Delivery.Project Management.Technical Project Management, AI Enablement, System Integration, Risk & Compliance.Compliance, Stackdriver, Prometheus, GitHub Actions, Containerization, Network Security, Networks, Cloudflare, AWS Certified DevOps Engineer, Policy as code (PaC), GitOps, Cloud Networking, IT Security, Cloud Monitoring, Dynamic Application Security Testing (DAST), Static Application Security Testing (SAST), ARM, Kubernetes Event-driven Autoscaler (KEDA), Azure Databricks, Azure Virtual Network (VNet), Gemini, LLM Agents, Palo Alto Networks, GPU Computing, Terraform Cloud, Network Load Balancing (NLB), Slackbot, Kyverno, Snyk, Trivy
How to Work with Toptal
Toptal matches you directly with global industry experts from our network in hours—not weeks or months.
Share your needs
Choose your talent
Start your risk-free talent trial
Top talent is in high demand.
Start hiring