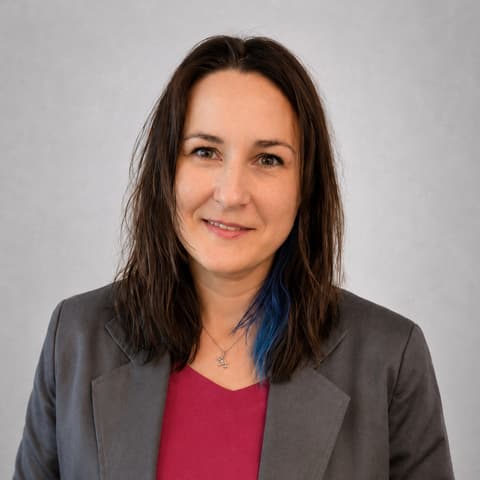
Mariia Tiurina
Verified Expert in Engineering
CloudSec Engineer and Developer
Tel Aviv-Yafo, Israel
Toptal member since July 14, 2026
Mariia is a senior application security engineer with over five years of experience in application and product security for clients such as Outseer, EPAM Systems, and OANDA. She specializes in threat modeling, secure design reviews, and vulnerability management for fintech and SaaS environments. Mariia won the Threat Modeling Hackathon at OANDA by building a reproducible research artifact that clearly separated discovery, exploit proof, and verdict.
Portfolio
Experience
- OWASP - 9 years
- CI/CD Pipelines - 8 years
- Web Application Security (Web AppSec) - 8 years
- GDPR - 7 years
- Dynamic Application Security Testing (DAST) - 7 years
- Amazon Web Services (AWS) - 5 years
- Static Application Security Testing (SAST) - 5 years
- SCA - 5 years
Preferred Environment
Amazon Web Services (AWS), Azure DevOps, Jira
The most amazing...
...project I've built is an intentionally vulnerable MCP server in Docker to explore AI tool security risks and validate real-world directory escape exploits.
Work Experience
Senior Application Security Engineer
Outseer
- Defined and executed the organization's application security strategy, aligning initiatives with business objectives and long-term risk management frameworks, and developed governance policies to ensure compliance with industry standards.
- Partnered with development teams of all seniority levels to address vulnerabilities, integrate security tools into CI/CD pipelines, and foster a proactive security culture by designing and implementing programs such as Capture the Flag events.
- Conducted advanced security assessments, including SAST, SCA, IaC, API security, and DAST; facilitated penetration testing, managed vendor relationships, and tracked remediation efforts using tools like Jira to ensure timely resolution of findings.
- Built and mentored high-performing security teams by fostering a culture of continuous learning and providing strategic guidance and hands-on expertise to empower developers and improve the organization’s security posture.
- Developed and presented key performance indicators to senior leadership to demonstrate the effectiveness of security initiatives and their impact on reducing risk.
- Communicated complex security issues clearly to executives and non-technical stakeholders and oversaw budgets and resource allocation for application security programs to ensure optimal efficiency and alignment with business goals.
Senior Systems Security Engineer
EPAM Systems
- Ran SAST, SCA, IaC, and API security scans on in-house developed code using Checkmarx and CheckmarxOne, and triaged scan results to identify true positives and false positives.
- Helped developers understand scan results and identify the best patch options.
- Advised developers on the nuances of setting pipelines in Azure DevOps to automate the scanning process.
- Developed interactive information security training for EPAM Summer School and taught more than 50 students per session.
- Performed threat modeling and prepared a recommendations report. Conducted baseline assessment and application design review, created design documents (DFD and C4 diagrams), and created an access control concept.
Information Security Analyst
OANDA
- Worked with on-premises and cloud-native security tools, including Rapid7, Splunk, CIS scanner, CarbonBlack, F5, among others.
- Ran regular security awareness sessions, designed a training plan for security onboarding in English and Polish, and onboarded over 200 people.
- Validated remediations of vulnerability findings using Nmap, SQLmap, Burp, and Burp Collaborator, among other tools.
- Maintained, managed, and monitored regional and local compliance to ISMS frameworks such as risk management, asset and access management, GDPR, and SOC2 regulatory and legal obligations.
InfoSec Analyst System Integration
Philip Morris International
- Provided IT security expertise throughout the implementation of new cloud-based SaaS and PaaS systems by performing security due diligence of potential vendors.
- Designed and documented an authorization concept (user and role definitions) in line with security requirements and best practices.
- Integrated with the company's identity and access management system.
- Implemented identity and access management in different IT systems.
- Performed criticality and risk assessments of services and systems together with business customers and embedded mitigating controls.
- Performed vulnerability scans and penetration tests for web-based applications in line with the OWASP methodology.
- Facilitated security scans performed by 3rd-party contractors, setting up the scope, reviewing results, and following up on remediation steps.
- Assured system compliance with corporate policies and procedures, FDA GxP regulations, and/or EU General Data Protection Regulation.
Experience
Vulnerability Management Program Design
I ran this exact program across PCI DSS, legacy, and shift-left products simultaneously—taking one environment from 30,000 unscoped findings to a clean pen test in 14 months.
AI/MCP Security Assessment
I do both: discovery scanning to map your attack surface, plus manual exploit validation to prove real impact, not theoretical risk. You get evidenced findings (request/response proof, CWE classification, severity) and concrete remediation steps—not just a list of warnings.
I built and published an open-source MCP security lab demonstrating a full discovery-to-exploit workflow against a real misconfiguration (CWE-22, path traversal)—the code and write-up are public on GitHub.
STRIDE and LINDDUN Threat Model
I use two frameworks together: STRIDE for technical threats (spoofing, tampering, privilege escalation, etc.) and LINDDUN for data privacy risks (consent, GDPR compliance, data exposure), so you get full coverage, not just half the picture.
Security Awareness Training
Topics I cover span social engineering and phishing recognition, password hygiene, MFA fatigue attacks, incident-reporting culture, and AI/LLM-related risks for employees who use AI tools at work.
I built a module around a real 2022 MFA-bypass breach at a major company, designed for non-technical audiences.
Security Policy and Compliance Documentation
I write policies based on your actual environment, including team size, tools, and data handled, mapped to the specific controls auditors check for, so you're not just compliant on paper. Common requests include an acceptable use policy, a password and access control policy, an incident response plan, a vulnerability management policy, a data classification policy, and a vendor risk policy.
Education
Bachelor's Degree in Mathematics
Pedagogical University of the National Education Commission in Kraków - Krakow, Poland
Certifications
Security And Compliance: Microsoft Security Center
Microsoft
Building Cloud-Native Applications Using Microservices Architecture
Microsoft
Microsoft Defender for Office 365
Microsoft
Threat Modeling Hackathon Winner
Threat Modelling Connect
AWS Security Certified
AWS
Certified In Cyber Threat Intelligence
Analiza
Special Recognition – EPAM Solution Architect Battle
EPAM Systems
OANDA Hackathon Winner
OANDA
AWS Certified Cloud Practitioner
AWS
Skills
Tools
Checkmarx, Invicti (Netsparker), Jira, SonarQube, Splunk, NMap, Sqlmap, Azure Kubernetes Service (AKS)
Paradigms
DevSecOps, Azure DevOps
Platforms
Amazon Web Services (AWS), Rapid7, Burp Suite, Azure, Docker
Industry Expertise
Cybersecurity
Languages
Python, MathML
Frameworks
Windows PowerShell
Other
OWASP, NIST, CI/CD Pipelines, Static Application Security Testing (SAST), SCA, Dynamic Application Security Testing (DAST), Regulatory Compliance, Web Application Security (Web AppSec), Threat Modeling, Security Architecture, Security, IT Security, OWASP Top 10, Application Security, Vulnerability Assessment, Consulting, Access Control, Information Security, GDPR, Infrastructure as Code (IaC), F5 Networks, SOC 2, IT Audits, AI Security, Compliance, Documentation, Cloud, SaaS, Startups, Endpoint Security, Large Language Models (LLMs), Artificial Intelligence (AI), Security Engineering, Identity & Access Management (IAM), SIEM, Microsoft Azure, Wiz Cloud Security Platform, CSPM, Prompt Engineering, Wiz.io, Crisis Management, Data Protection, Governance, Security Audits, Responsible AI, AWS Cloud Security, Enterprise Cybersecurity, Vulnerability Management, Risk Assessment, Security Policy Analysis, MCP Security, AI Trust, Risk and Security Management (AI TRiSM), LLM Security, STRIDE, Enterprise Security Architecture, General Data Protection Regulation (GDPR), Secure Coding Training, Security Awareness Training, Phishing Simulation & Analysis, Onboarding, Security Policies & Procedures, ISO 27001, PCI DSS, Process Flows, Threats, Threat Intelligence, Cyber Defense, Threat Detection and Response (TDR), Azure Cloud Security, Cloud Security, Microsoft Defender XDR, Microsoft Defender Antivirus, LLM Fine-tuning, IT Projects, IT, Education Technology (Edtech), Agentic AI, AI Agents, Prompt Injection, Multi-agent Systems, Incident Response, AI Governance, PCI DSS ISA
How to Work with Toptal
Toptal matches you directly with global industry experts from our network in hours—not weeks or months.
Share your needs
Choose your talent
Start your risk-free talent trial
Top talent is in high demand.
Start hiring