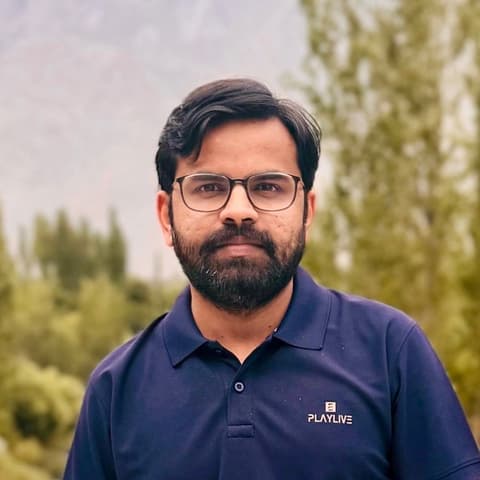
Usman Arif
Verified Expert in Engineering
Offensive Security Consultant and Developer
Islamabad, Islamabad Capital Territory, Pakistan
Toptal member since June 16, 2026
Usman is an offensive security consultant specializing in penetration testing and adversary simulation for enterprise organizations. With 8+ years of experience across financial, telecom, government, and technology sectors, he helps clients uncover critical attack paths and strengthen their security posture through practical, risk-driven recommendations. Usman provides practical, risk-driven recommendations that fortify defenses and improve overall cybersecurity resilience.
Portfolio
Experience
- Vulnerability Assessment - 9 years
- Web App Security - 9 years
- IT Security - 9 years
- Network Security - 8 years
- SOC 2 - 8 years
- Application Security - 8 years
- Cloud Security - 8 years
- Penetration Testing - 8 years
Preferred Environment
Penetration Testing, Information Security, Vulnerability Assessment, AI Security, Mobile App Security, IT Security, Vulnerability Scanning, SOC 2, HIPAA Compliance, Application Security
The most amazing...
...security test I've done was an app security assessment that identified an authorization weakness that allowed privilege escalation via API request manipulation.
Work Experience
Independent Offensive Security Consultant
Self-employed
- Provided independent security assessment services to different clients across the globe.
- Conducted web, mobile, API, and infrastructure security assessments to identify and prioritize critical risks.
- Evaluated AI-enabled applications and modern authentication workflows for emerging security risks.
- Led red team and adversary simulation engagements to evaluate organizational resilience against real-world threats.
- Assessed Active Directory and enterprise environments for privilege escalation and attack path exposure.
- Performed cloud and SaaS security reviews to strengthen security posture and configuration management.
- Produced technical and executive-level reports with actionable remediation recommendations.
Offensive Cybersecurity Consultant
Help AG (An e& Company)
- Delivered offensive security engagements for enterprise clients across highly regulated industries.
- Conducted external, internal, application, API, and Active Directory security assessments across complex environments.
- Led red and purple team exercises to simulate realistic adversary behavior and evaluate defensive capabilities.
- Identified critical attack paths and collaborated with stakeholders to prioritize remediation efforts.
- Assessed enterprise infrastructure and cloud environments for security weaknesses and configuration risks.
- Produced technical and executive-level deliverables to support informed risk management decisions.
- Supported threat simulation activities that strengthened detection and incident response capabilities.
Cyber Security Consultant
Supersecure
- Delivered security assessments across web, mobile, API, cloud, and SaaS environments, identifying vulnerabilities and practical attack paths.
- Conducted application and infrastructure penetration tests to identify authentication, authorization, configuration, and access-control weaknesses.
- Assessed cloud and SaaS environments for security misconfigurations, exposed services, and weaknesses affecting organizational security posture.
- Collaborated with technical stakeholders to translate security findings into practical remediation strategies and risk-reduction measures.
Team Lead, Security Assessment
Trillium Information Security Systems
- Delivered security assessment engagements for more than 50 financial, telecommunications, and public sector organizations.
- Led application and infrastructure penetration testing projects while coordinating technical delivery and client communication.
- Defined assessment scope and testing strategies to align security objectives with business requirements.
- Identified high-impact security weaknesses across enterprise applications and network environments.
- Produced technical and executive-level reports with practical, risk-based remediation recommendations.
- Mentored team members and contributed to the successful execution of complex offensive security engagements.
- Bridged technical and business requirements by collaborating with stakeholders throughout project lifecycles.
Experience
Web Application Authorization Security Assessment
I evaluated access control implementation and provided remediation guidance to strengthen server-side authorization and application security based on the school manager privilege escalation scenario.
Enterprise Active Directory Attack Path Assessment
I evaluated authentication weaknesses and identified privilege escalation opportunities, and provided remediation strategies to reduce enterprise risk based on the JMX-to-ADCS scenario.
Enterprise Wireless Security Assessment
I also delivered practical recommendations to strengthen authentication and wireless security controls derived from the wireless credential capture and MSCHAPv2 scenario.
Internal Network Segmentation Security Review
Education
Bachelor's Degree in Telecommunications Engineering
Foundation University Islamabad - Islamabad, Pakistan
Certifications
Certified Red Team Operator (CRTO)
Zero-Point Security
Certified Mobile Security Expert (CMSE)
8ksec
API Penetration Testing
APIsec University
eLearnSecurity Web Application Penetration Tester eXtreme (eWPTXv2)
INE Security
Offensive Security Certified Professional (OSCP)
Offensive Security
Certified Penetration Testing Engineer (CPTE)
Mile2
Skills
Libraries/APIs
REST APIs, GraphQL API
Tools
Metasploit, OWASP Zed Attack Proxy (ZAP)
Paradigms
Penetration Testing, HIPAA Compliance, Server Message Block (SMB)
Platforms
Burp Suite
Industry Expertise
Cybersecurity
Languages
Python
Other
Red Teaming, Cloud Security, Active Directory (AD), Information Security, Vulnerability Assessment, IT Security, Web Application Security (Web AppSec), APIs, Mobile App Security, Network Security, Open-source Intelligence (OSINT), Network Exploitation, Vulnerability Scanning, Adversarial Testing, Ethical Hacking, OWASP Top 10, Exploits, Wireless Security, SOC 2, OSCP, Security Engineering, Application Security, Web Security, Compliance, Certified Ethical Hacker (CEH), AI Security, OT Security, Project Leadership, Exploit Development, Privilege Escalation, Mobile Security, MITRE ATT&CK, IT Infrastructure, linux security, Command and Control, Security, Authentication, Authorization, Reverse Engineering, Web App Security, Active Directory Security, Cobalt Strike, Zero-day Vulnerabilities, Cloud Infrastructure, Burp Proxy
How to Work with Toptal
Toptal matches you directly with global industry experts from our network in hours—not weeks or months.
Share your needs
Choose your talent
Start your risk-free talent trial
Top talent is in high demand.
Start hiring